The inaugural edition · 2026
Behind every app you trust stands a security mind.
The AppSec 30 celebrates thirty application security leaders for the work that keeps the apps millions of people rely on safe. This is their list, and their stories.
- Nominated, never bought
- No fees, no sponsorships
- Celebrated on Times Square
- 01
- 02
- 03
- 04
- 05
- 06
- 07
- 08
- 09
- 10
- 11
- 12
- 13
- 14
- 15
- 16
- 17
- 18
- 19
- 20
- 21
- 22
- 23
- 24
- 25
- 26
- 27
- 28
- 29
- 30
Thirty places. Revealed one leader at a time.
Why AppSec30
Finally, the recognition AppSec leaders deserve.
The people who secure the apps we all live inside do some of the most consequential work in technology. They build the programs, train the teams, find the flaws first and shape how an entire industry ships safer software.
And when they do it well, nobody notices. A breach that doesn't happen makes no headline. The AppSec 30 brings thirty of them onto one list, to celebrate what they have built and to share how they think, so the next generation can see who to become.
Nominated
Put forward by people who know the work, and read by our team, every one.
No fees
No sponsorships, nothing to buy. A place on this list cannot be bought.
Contribution
Recognized for what they built and gave back: programs, research, tools and people.
2026
The inaugural edition, assembled now, by invitation.
Why it matters now
Software runs the world. Someone has to make sure it holds.
More code ships every day, more of it is written by AI, and attackers move just as fast. These are the odds the AppSec 30 beat, every day.
48,185
CVEs published in 2025, about 131 new vulnerabilities every day.
Jerry Gamblin, 2025 CVE Data Review
20%
of breaches now begin with an exploited vulnerability, up 34% in a year.
Verizon DBIR 2025
$4.44M
average cost of a data breach worldwide, and $10.22M in the US.
IBM Cost of a Data Breach 2025
45%
of AI coding tasks produced code with a security vulnerability in it.
Veracode GenAI Code Security Report 2025
1 : 24
one software security professional for every 24 developers, at the companies taking it most seriously.
BSIMM15
4.8M
cybersecurity roles the world still needs to fill.
ISC2 Workforce Study 2024
From Appknox's own scans, 2025
346,874
vulnerabilities found across more than 50,000 scans, 83,887 of them critical or high. Behind every one fixed before release is someone nobody will ever thank. Until now.
The honorees
Thirty leaders. One craft.
The people who run application security for some of the most consequential apps in the world, recognized in one place. Honorees are revealed one at a time, with their approval.
Already accepted by leaders from
What every honoree receives
Their story, told properly.
A published feature
A profile of their career and leadership, published only once they have approved it.
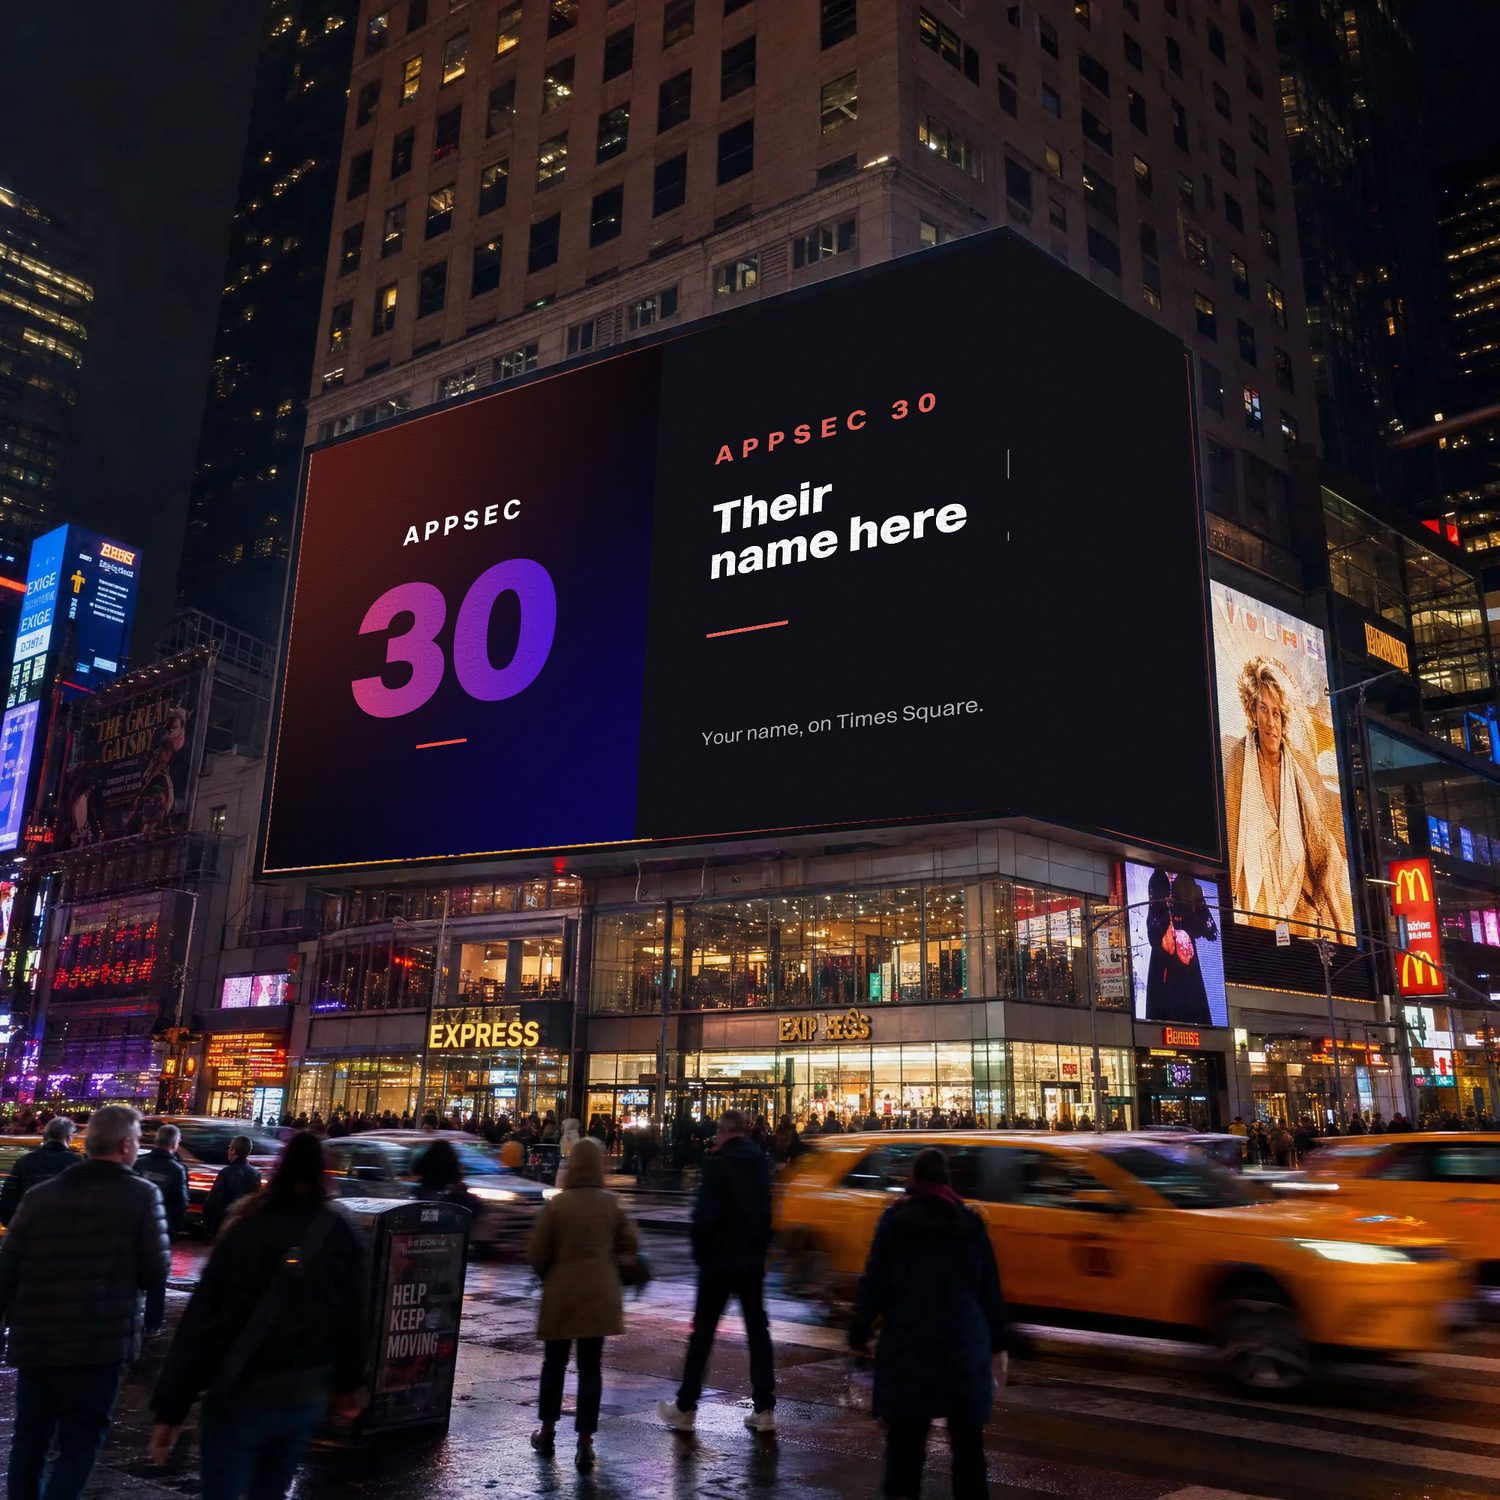
Their name on Times Square
In lights, on the screens the whole industry walks past.
A podcast episode
Their story, in their own words, for the practitioners deciding who to become. Nothing airs until they approve it.
The AppSec 30 magazine
Their work, in print and on the record. Nothing goes to press without their sign-off.
How it works
Nominated by the people who know the work.
- 01
Nominated
Anyone can put forward the leader who shaped how they, or their team, secure software. It takes a name and an email.
- 02
Reviewed
We read every nomination ourselves, and reach out personally to the leaders who make the shortlist.
- 03
Celebrated
Each honoree is revealed with their story and a place among the thirty, and nothing is published without their approval.
Know a security mind who belongs here?
Nominations for the inaugural 2026 edition are open. It takes thirty seconds, and it might be the first time someone tells them their work mattered this much.
Nominate a leader
Questions
Before you nominate.
Who can be nominated?
Anyone whose work has made application security better: program leaders, architects, engineers, researchers, educators and founders. Title matters less than impact.
What happens after I nominate someone?
We read every nomination ourselves. Leaders who make the shortlist hear from us personally, with an invitation that explains everything before they decide.
Will they know who nominated them?
Nominations from this page are anonymous. We only use their email to reach out about the AppSec 30.
Does it cost anything?
No. There is nothing to buy and no product in it. Appknox pays for the AppSec 30 because the profession deserves it.
Will they be asked to share anything confidential?
Never. No client information, internal architecture, incidents or proprietary processes, and nothing is published without their review and approval.